In this issue
The big story
Let me say up front what this issue is not.
I am not on the bandwagon that worries AI will end the world. The largest labs have real safety responsibilities. They also have liability and market incentives that do not always line up with the needs of a smaller business, and I do not need to settle anyone's motives to run my own company well.
My concern is more practical. I am giving software agents authority to change things: records, schedules, code, messages. When one of them gets something wrong, I want to trace exactly what happened without asking the agent to remember.
Here is what taught me that. I recently found a monitoring job that looked complete on paper. The scanner existed. The schedule existed. The reporting path existed. The controls had even passed a manual test.
But the scheduled run had been failing silently.
Nothing was missing from the feature list. What was missing was the ability to tell configured from working. A dashboard would have shown the last good result. It would not have proved that the current run happened.
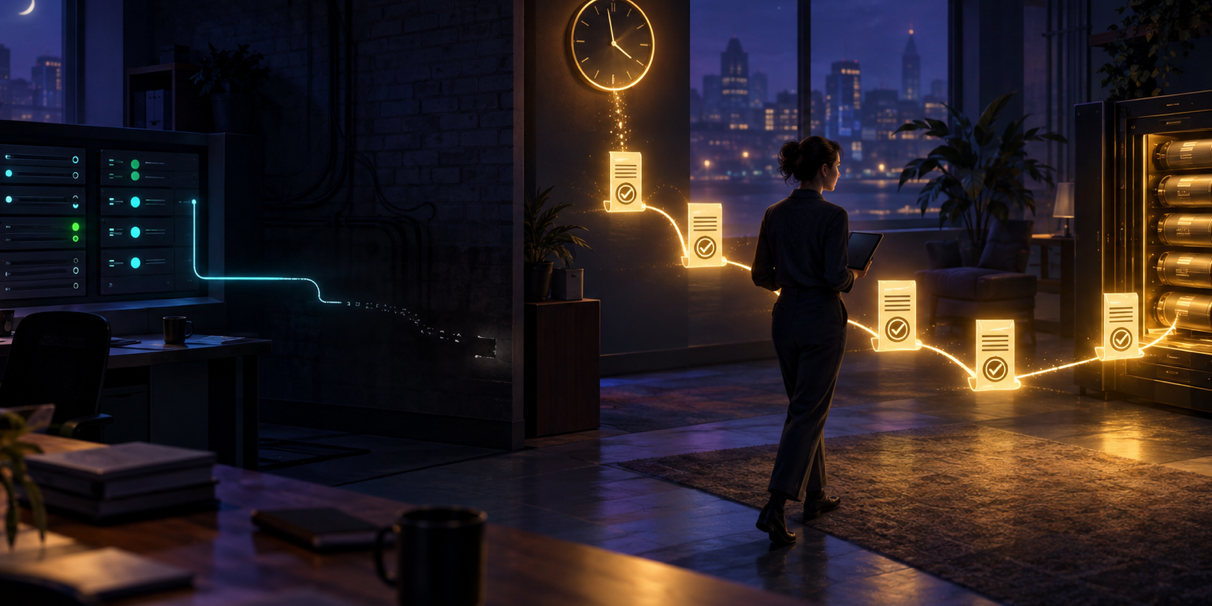
What I needed was the business equivalent of an aircraft's flight recorder: an append-only record of what the agent intended, the authority it relied on, what it changed, and the evidence that the result actually occurred. My agents have since built the tamper-evident backbone for that inside my own company, and I am now building the fuller receipt around it so each consequential action carries the business context needed to explain it.
We are giving probabilistic systems access to deterministic business consequences. In plain terms, software that is sometimes wrong now has the power to do things that are hard to undo. The record between those two worlds cannot be an afterthought.
The record
A log is not a black box
Most software already produces logs. A log can show that an API returned 200 or a job exited cleanly. After an incident, those facts rarely answer the questions that matter: What was the agent trying to do? Who authorized it? What changed outside the model? Was the result verified, or just reported as done? Can it be reversed?
The useful record is not a dump of the model's hidden reasoning. That material is noisy, sensitive, and a poor audit artifact. The useful record has two layers: a structured action receipt that explains the business event, and a set of linked fingerprints that makes a rewritten history detectable.
Framework spotlight · The control standard I am building around my existing ledger. A pattern, not a product.
Agent action receipt
The minimum record for consequential work
Nothing makes a file impossible to change. The linked fingerprints make a change impossible to hide. In my own company the rule is simple: if the record fails its own check, agents that work through my controls stop consequential work until I understand why.
One field in the receipt does more work than any rollback plan: can this be undone? Most agent work is reversible for free, a file edit with history or a draft that has not gone anywhere. Some is reversible with effort, and for those the trace is enough to design the rollback if the day comes. Some cannot be undone at all: a sent email, a payment, a deletion, a public post. Nothing recovers those, so they get a gate in front of them instead of a plan behind them. A gate is anything that makes the action wait for a decision the agent cannot make alone: a person who approves it, a dry run that shows what would happen first, a staging copy someone reviews, or a limit the agent cannot raise on its own.
Most small businesses do not need an exotic ledger on day one. They do need the entries linked from day one if they want to call the record tamper-evident. Signed snapshots and independent time-stamping can come later. Write the receipt in language a person can read, not compressed agent shorthand. If a customer or a vendor ever disputes what your system did, this record is what you fall back on.
The release decision
Now you can see what happened. Should it have shipped?
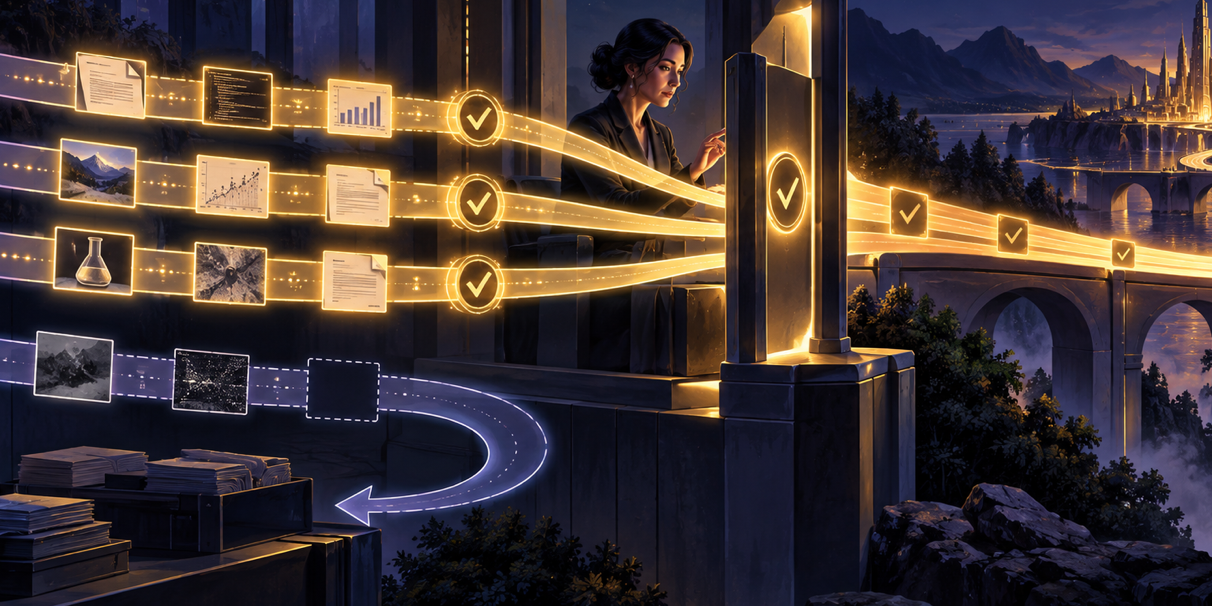
A ledger explains the past. It does not tell you whether the next change is ready to go out. That is where a release score comes in.
I have been evaluating AI code-review tools that map a whole repository and score a pull request against it. That is a useful outside challenge, and every business should evaluate the category for itself. But a code reviewer cannot prove the whole business workflow. It cannot prove that a scheduled job is still alive, that a vendor deleted the right data, or that production matches the branch it reviewed.
So the decision is not "buy a reviewer or build a framework." It is: own the release standard, attach evidence to every score, use outside reviewers to challenge the evidence, and let a failed dimension block the release.
Here is what that looks like in my own shop. Agents work around the clock and never wait on me. But a newsletter, an email, or a code change does not leave the building until a person has reviewed the finished work in a staging copy and approved it. The agents keep producing. The release waits.
This is not a five-star rating. The threshold follows the consequence.
A drafting assistant can ship at a lower score than an agent that moves money, edits a customer record, or sends a message in someone else's name.
The checks
Make the expensive promises checkable
A score is only as good as the things you can check. Mathematically checked software has a pattern worth borrowing. The clearest example is Lean, a programming language and theorem prover whose small trusted kernel can check model-generated formal proofs. You do not need Lean to borrow the pattern. You need the habit: state the promise precisely enough that code, not a person reading a chat window, can confirm it. Formalizing an entire business that way is a mistake. The narrow version works.
Instead of telling an agent, "Be careful with refunds," write the contract:
- the amount must be under the employee's authority limit;
- the customer and transaction must match;
- the transaction must not already be refunded;
- the payment provider must return a durable confirmation.
The generative model interprets the messy request. Deterministic code checks the contract. A human handles the ambiguous or expensive exception. In most businesses that code is a database rule, a schema check, or a test that runs before anything ships.
Continuity
Keep one lane you control
Everything above assumes you can keep operating. Being unworried about the end of the world does not mean being unworried about depending on one provider. Call it concentration risk. Providers change prices. Models get retired. Access rules narrow. A capability that is acceptable today may fall outside a provider's risk posture tomorrow.
Maintain one useful lane the business controls: a local model for bounded internal work, owned hardware or a portable environment, narrow credentials, explicit budgets, and an action ledger that no single provider can rewrite.
Local does not mean safe. A local model with administrative permissions can damage a business as efficiently as a remote one. What you gain is control over whether you keep operating, where your data and models live, and what evidence you hold.
One thing to try this week · The 45-minute move
Record one consequential workflow
Choose one AI workflow that can change something outside the chat window.
- Write the one-sentence intent.
- Name the first consequential action.
- Record the authority required for that action.
- Capture the before-and-after environmental state.
- Attach the verification evidence.
- Note whether the action can be undone. If it cannot, put a gate in front of it: a person's approval, a dry run, or a limit the agent cannot raise.
- Score the workflow from 0 to 5 and leave unsupported dimensions blank.
Then ask one person or one independent model to challenge the weakest claim. The missing evidence will tell you what to build next.
Worth watching
What I am watching
The next durable advantage will not belong to the business that gives agents the most freedom. It will belong to the business that can increase autonomy without losing the ability to explain, stop, and recover the work.
Reader question · A starter black box
Want a starter black box for your own agents?
I am considering publishing a free starter version of the black box you have been reading about: linked receipts, a way to verify them, and instructions for keeping a copy you control.
It is not released yet, and I have not decided whether it should be a bonus resource, an open toolkit, or a fuller product. Would you use it? Reply to this email, or leave a comment on whichever platform you are reading this, with the workflow you would want it to protect. Those answers will decide what is worth releasing.
Why Obsidian Insights
I started Obsidian Insights to bring enterprise-grade operating discipline to businesses that cannot hire a platform team. As agents gain authority, that discipline begins with a record the agent cannot quietly rewrite.
Sources and notes
- William McBride's owner-authored operating reflection, recorded September 22, 2026. This edition represents William's synthesis and recommendations.
- Lean Language Reference: official description of Lean as an interactive theorem prover used in mathematics and software verification. Referenced as the source of the pattern, not as a recommendation to adopt Lean.
- The other product categories referenced (AI code review, local model runtimes) were checked against the vendors' own public documentation. No vendor is named or endorsed.